Security questionnaire automation
Hours, not days, on a security questionnaire
A security questionnaire is answered from evidence your team has already approved. This page is the workflow: how a SIG, CAIQ or a buyer's own spreadsheet goes from intake to submission, what happens at each step, who touches it, and what it connects to.
The workflow, start to finish
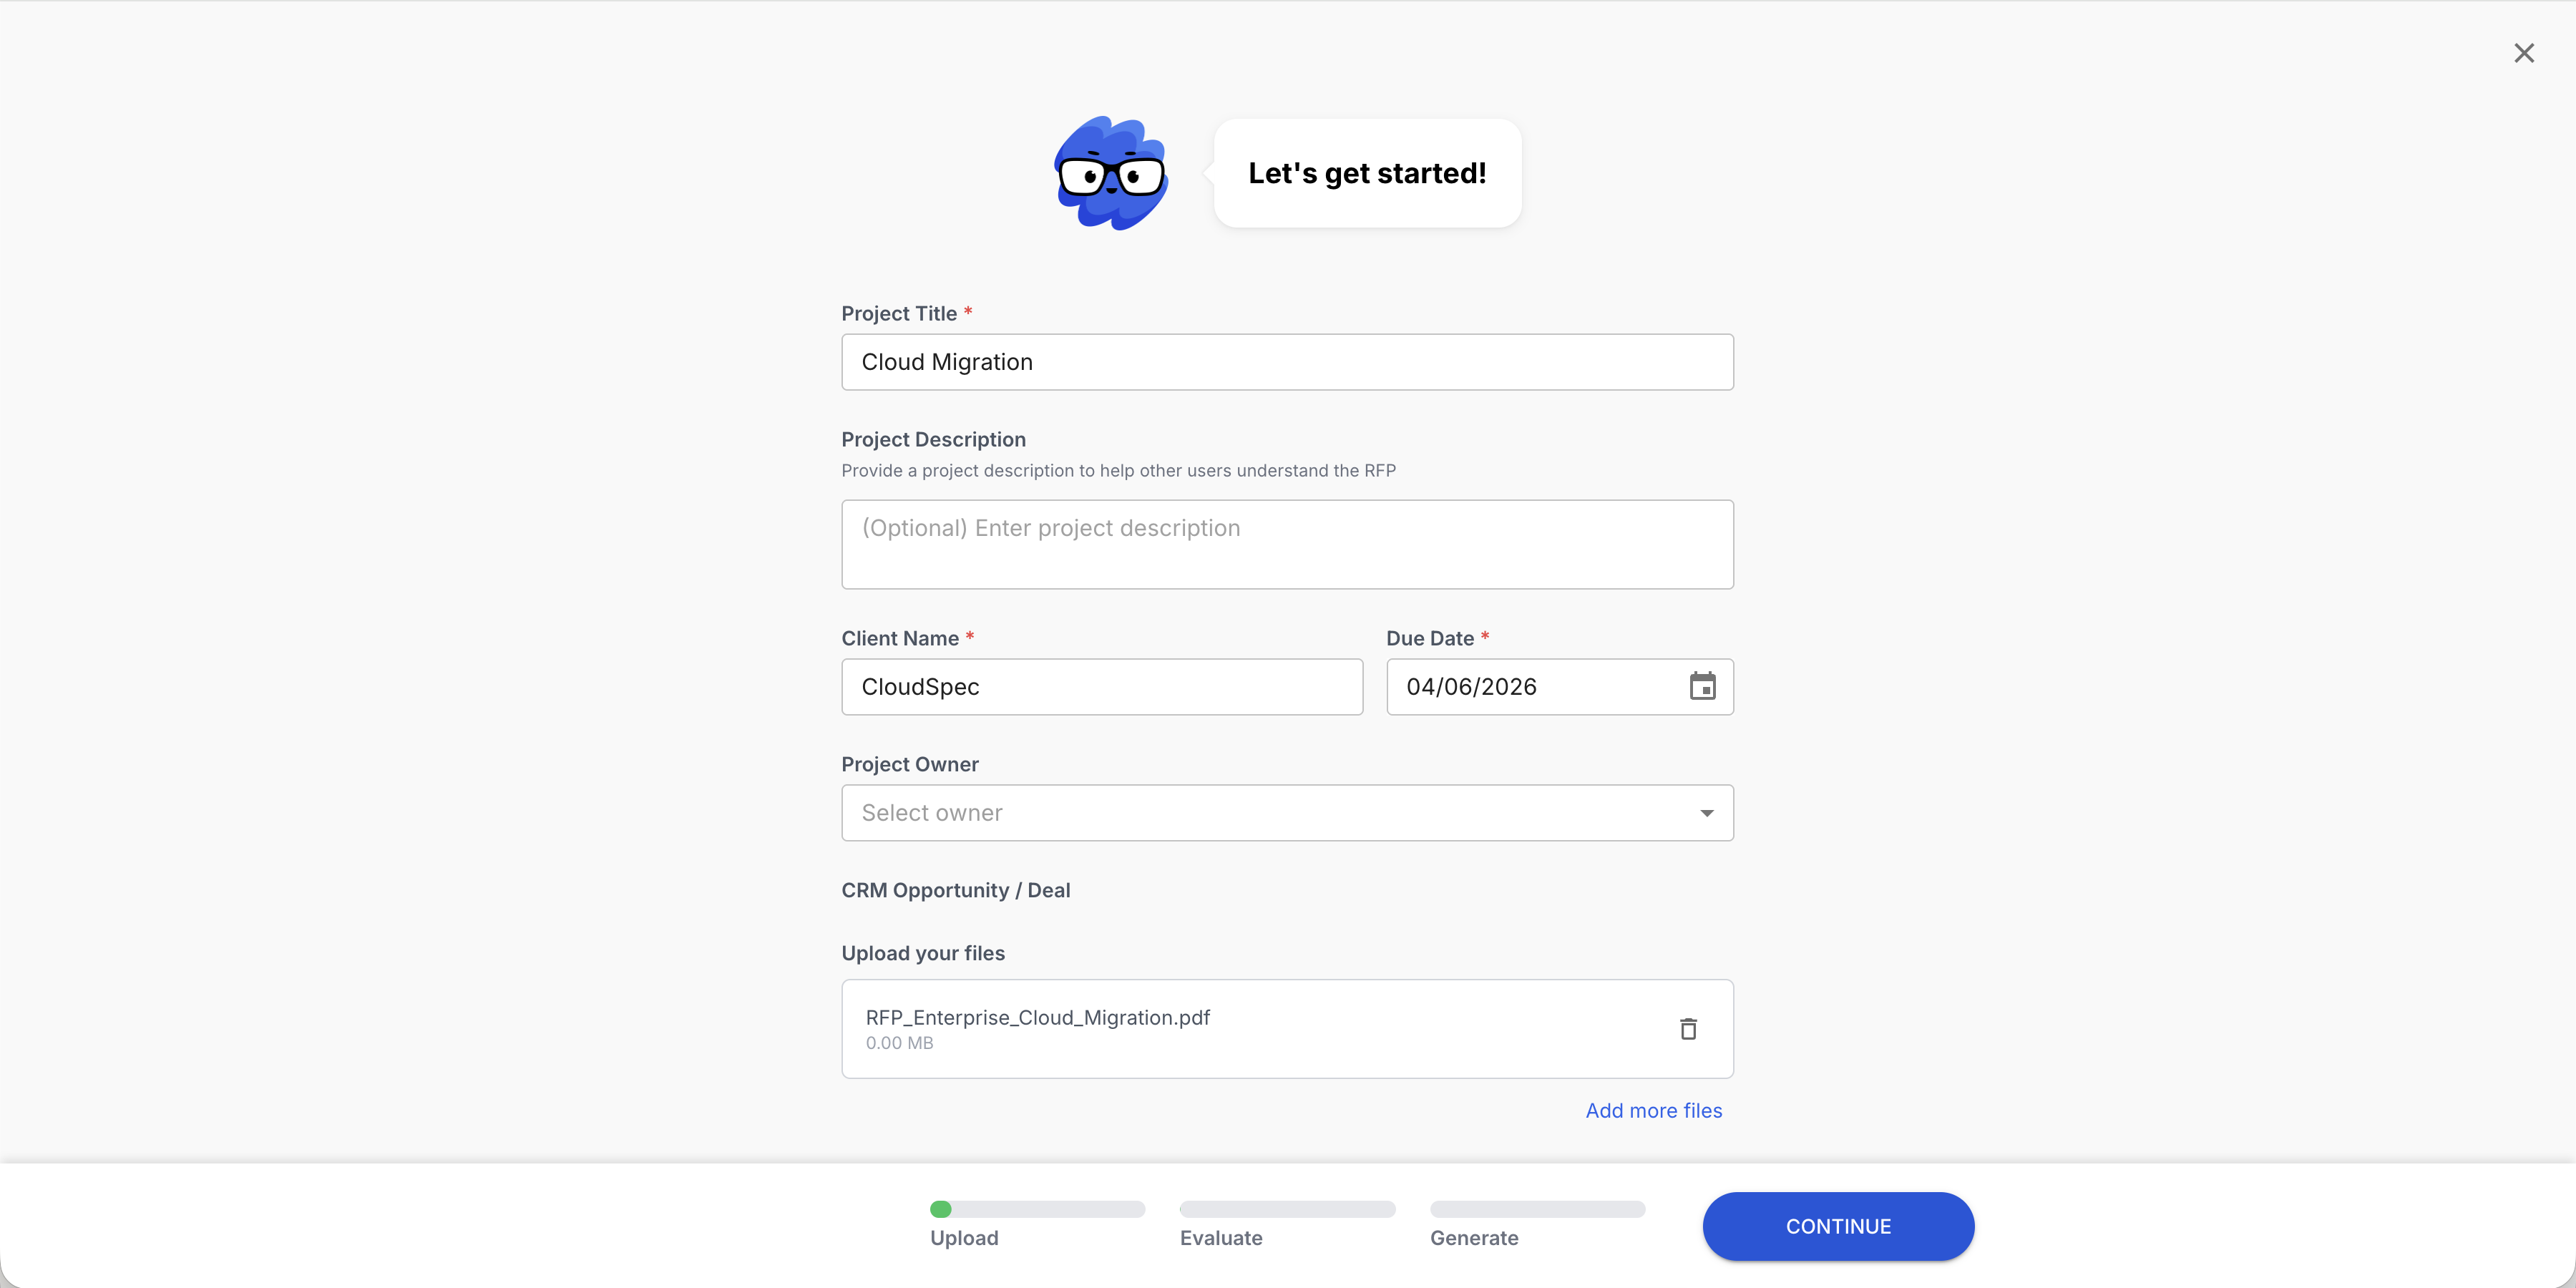
Five steps. The first three are automatic, the fourth is where your security team spends its time, and the fifth is what stops a contradiction reaching the buyer.
- 01
Intake, any format
SIG Lite, SIG Full, CAIQ, VSA, a spreadsheet, a document or a portal export. The question and answer structure is parsed regardless of format, and each question is classified by control area.
- 02
Retrieval from approved evidence
Each question is matched against approved content: policies, SOC 2 evidence, certification scope and prior responses. Retrieval is permission aware, so a reviewer sees only evidence they are entitled to.
- 03
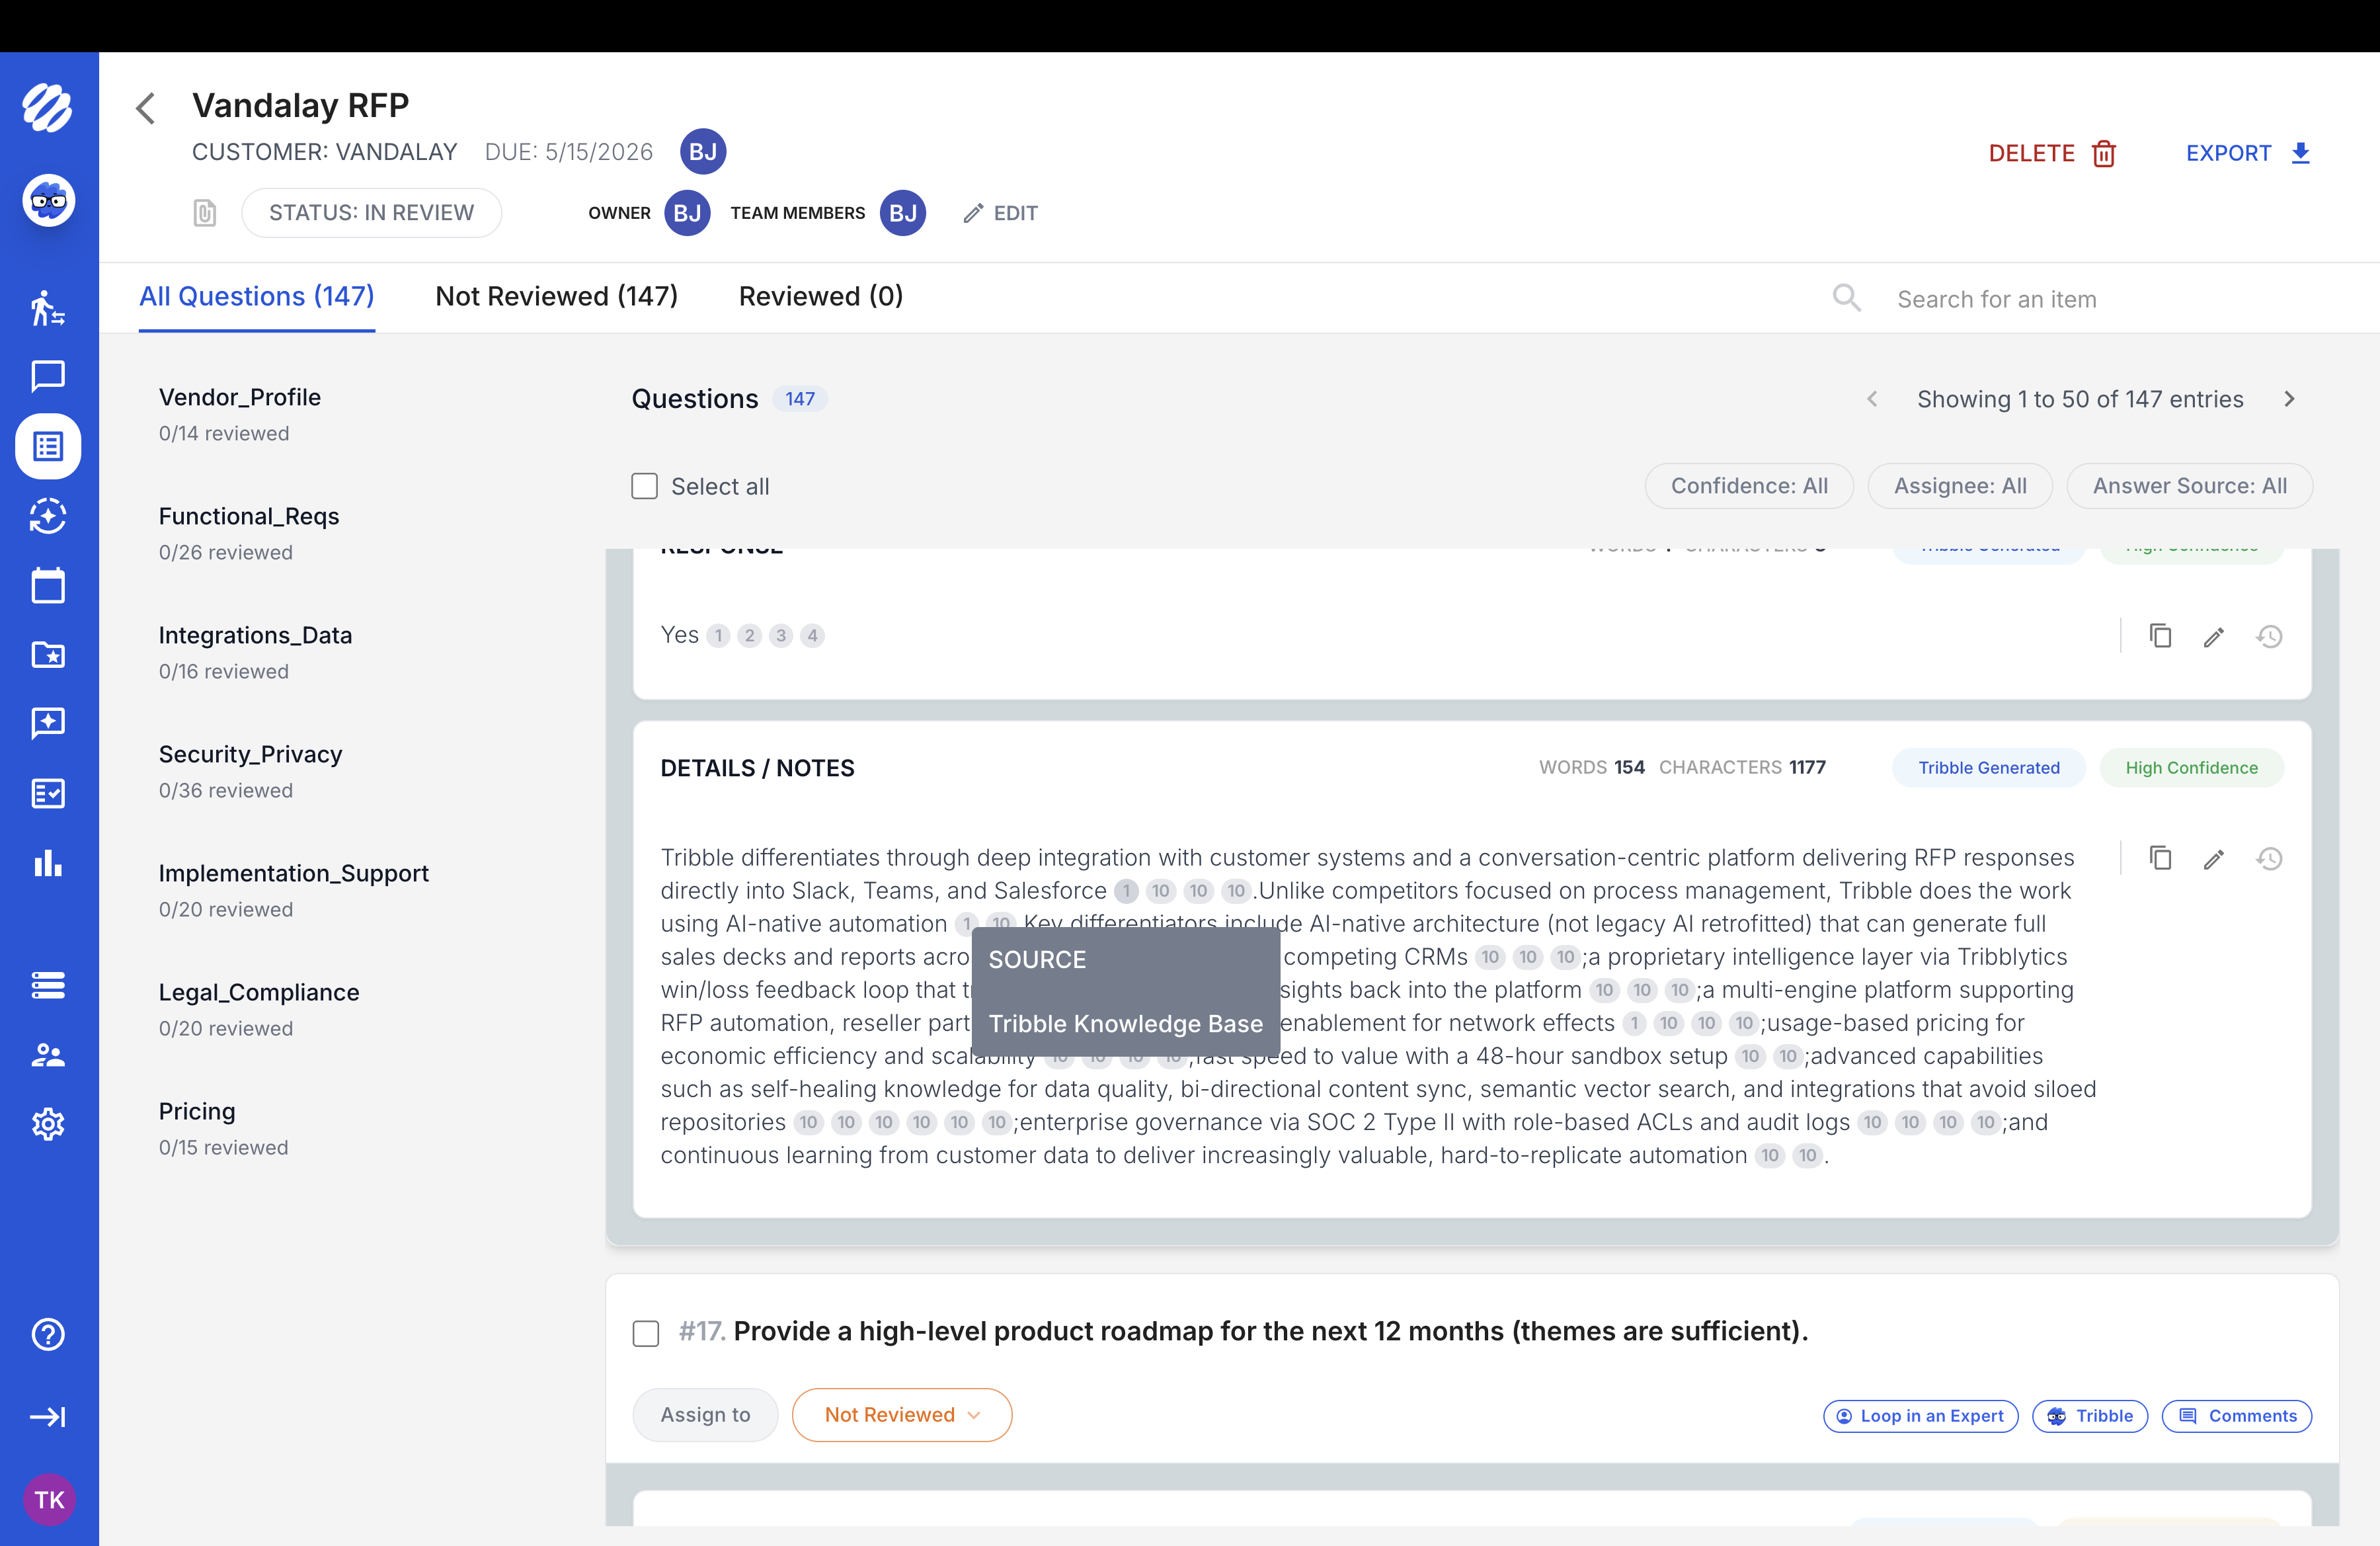
A draft with the source attached
Each answer names the document it came from and carries a confidence level. It is written for the evaluator reading it rather than as a restatement of the question.
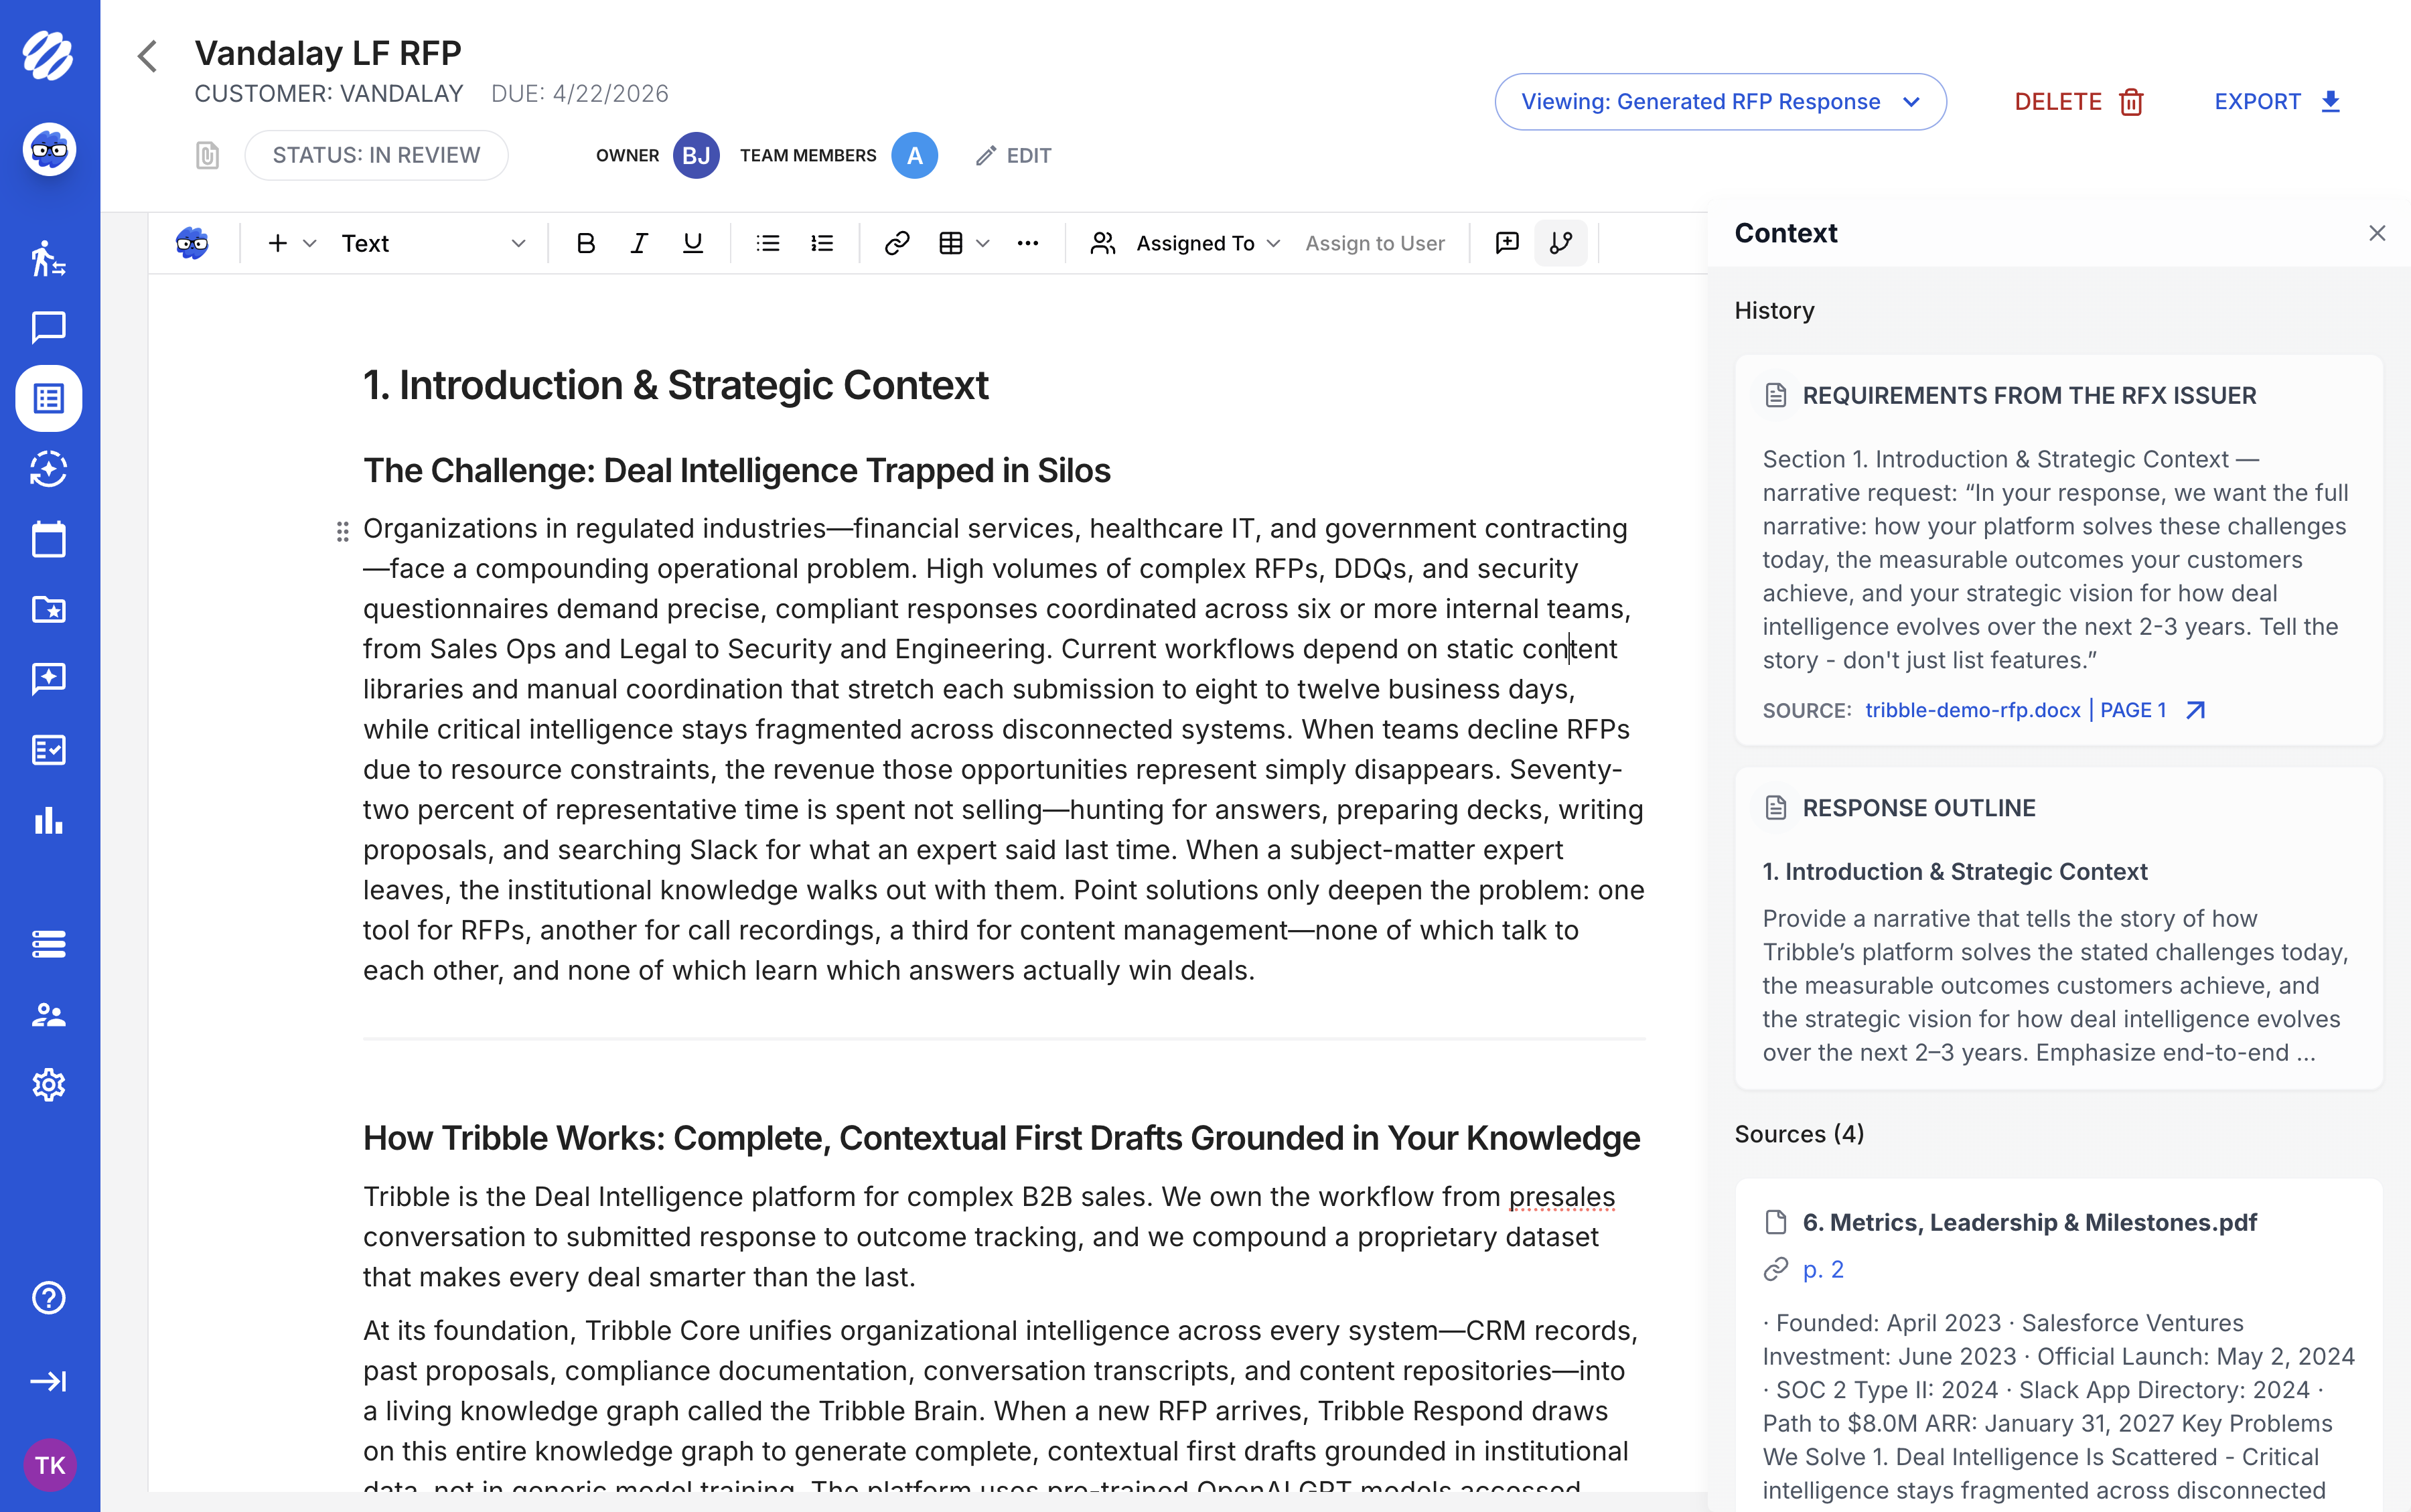
- 04
Review, and routing for what needs an owner
Confidence decides what a human sees. Anything the approved content does not cover goes to the control owner in Slack or Teams, with the question, the context and the evidence found so far.
- 05
Consistency check, then submit
Every answer is checked against every other answer, so contradictions across 200 or more items surface before the buyer sees them. The approved response is kept, so the next questionnaire starts from it.
What the system does at each step
Per-answer confidence
Every draft carries its own confidence level, so a reviewer can see which answers are ready and which need an expert, rather than reading all 200 at the same depth.
Cross-answer consistency check
Every answer is compared against every other answer in the questionnaire. Contradictions across 200 or more items are surfaced before submission rather than found by the evaluator.
Buyer-aware drafting
Answers are drafted with the engagement context, so a response addresses what the evaluator is assessing rather than restating the question.
Permission-aware retrieval
Access follows your existing permissions and roles. Evidence a reviewer cannot open does not appear in a draft they can.
Approved answers are kept
Once a reviewer approves an answer it becomes approved content. The next questionnaire starts from it instead of from a blank page.
Formats and frameworks it takes
Intake is format-agnostic because the parser reads the question and answer structure rather than the template.
| Arrives as | Handled |
|---|---|
| SIG Lite and SIG Full | Parsed by control area, mapped to approved evidence per question |
| CAIQ | Parsed by control area; prior CAIQ responses are reused where approved |
| VSA and vendor risk assessments | Parsed as a questionnaire; unmapped questions route to the control owner |
| A buyer's own spreadsheet (XLSX) | Question and answer columns detected, answered in place |
| DOCX and PDF | Questions extracted, answered, exported in the original structure |
| Vendor portal | Direct portal intake, so answers do not have to be pasted twice |
10-20% of security responses needed specialist review
The rest came back from approved content. Clari’s numbers, from their published story.
How it differs from the alternatives
Three things teams use instead, and what each one leaves you doing by hand.
| Tribble | A compliance platform | A content library | General-purpose AI | |
|---|---|---|---|---|
| What it is for | Answering the questionnaire | Collecting evidence and monitoring controls | Storing approved answers | Drafting text |
| Source on each answer | Named document per answer | Not its job | Manual reference | None |
| Per-answer confidence | Yes | No | No | No |
| Routing to the control owner | By control area, in Slack or Teams | Alerts on controls | Alert-based | None |
| Consistency across the questionnaire | Checked across every answer | No | No | No |
| Improves with each questionnaire | Approved answers are kept and reused | Not its job | Library needs upkeep | No memory between sessions |
A compliance platform and Tribble are complementary. One is the system of record for your posture; the other answers the questionnaires that follow from it.
What happens when a claim is challenged
A single unverified claim, an out-of-date policy or a misremembered certification scope, can fail an assessment and restart procurement. The workflow is built so that a challenged answer is answerable.
The answer names its source
Not a reference list at the end of the document. The specific policy, control or prior response that answer was drafted from, attached to that answer, so an evaluator asking "where does this come from" gets a document rather than an assurance.
The reviewer is recorded
Who approved the answer and when. If the claim turns out to be wrong, the question is which evidence was current at the time rather than who typed it.
Scope is stated, not implied
Certification scope is drawn from the report rather than paraphrased, so an answer does not quietly widen what a certificate covers. This is the failure that costs the most and it is a wording problem, not a control problem.
Nothing is answered that cannot be sourced
Where the approved content does not cover the question, it is routed rather than filled. An unanswered question returned to a control owner costs a day. A confidently wrong one can cost the deal.
Where the evidence already lives
Retrieval reads from your existing systems rather than asking you to move anything into a new one. Policies and evidence from the first five, deal context from the CRM, routing through Slack or Teams.


Questions people ask before a first questionnaire
The ones that come up on nearly every call.
How do you automate security questionnaire responses?
Upload the questionnaire in any format. Each question is classified by control area and matched to approved security content: policies, SOC 2 evidence and prior responses. The draft comes back with the source document named on each answer and a per-answer confidence level. Reviewers verify sourced evidence rather than unattributed output, anything the approved content does not cover is routed to the control owner, and a consistency check runs across the whole questionnaire before submission.
What questionnaire formats are supported?
SIG Lite, SIG Full, CAIQ, VSA, XLSX, DOCX, PDF, and direct portal intake. The question and answer structure is parsed automatically regardless of format, so a buyer's own spreadsheet works the same way as a standard framework.
How is this different from a compliance platform?
A compliance platform collects evidence and monitors controls. It is the system of record for your posture. This answers the buyer questionnaires that follow, by drafting from that evidence, your policies and your prior responses. The two are complementary, and most teams running one still answer questionnaires by hand.
How do you know the answers are right?
Every answer names the document it was drafted from and carries a confidence level, so a reviewer approves a sourced answer rather than an assertion. Answers the approved content does not cover are flagged rather than guessed, and the consistency check catches contradictions across the questionnaire before anyone outside sees it.
What does it connect to?
The places security evidence already lives: SharePoint, Google Drive, Confluence, Notion and Box for policies and evidence, Salesforce and HubSpot for deal context, and Slack and Microsoft Teams for routing questions to the control owner.
Can it answer SOC 2 questionnaire responses?
Yes, where your SOC 2 report and the policies behind it are connected as approved sources. Answers cite the specific control, for example CC6 for access control, so a reviewer can check the claim against the report rather than take it on trust.
What happens to questions nobody has answered before?
They are routed, not guessed. The question goes to the control owner in Slack or Teams with the context and whatever evidence was found, and once they answer it the response is kept as approved content for the next questionnaire.
How long does onboarding take?
A team can run a real questionnaire as soon as source access is connected and the first evidence is indexed. The quality of the first draft depends on how much approved content exists, not on how long the system has been running.
How does pricing work?
Priced per Seller and per Project rather than per questionnaire. The right model depends on questionnaire volume, hours per review and how much work moves from drafting to verification, so we price against your volumes on the call rather than putting a figure on a page.
Related
Tribble Respond is the product this workflow runs on, alongside RFPs, long-form responses, DDQs and portal intake. DDQ automation is the same workflow against due diligence questionnaires. The guide to security questionnaire automation covers the category rather than the product.